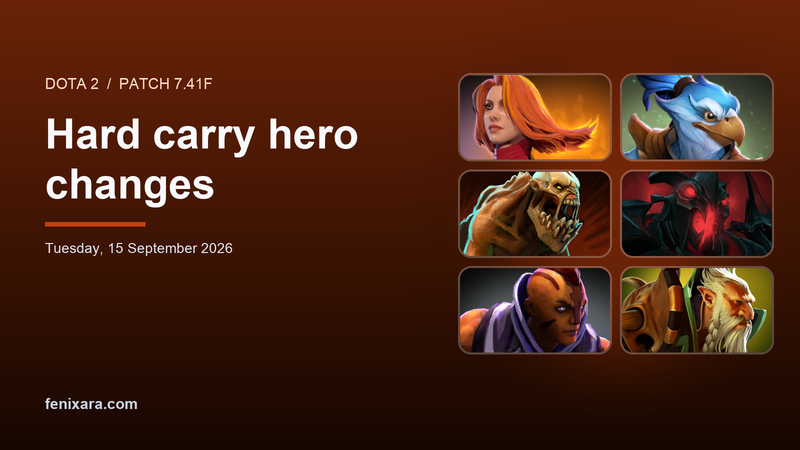
Dota 2 patch 7.41f hard carry hero changes
Every hard carry hero changed in Dota 2 patch 7.41f (8 heroes), with the full change list and my take on each one.


Every hard carry hero changed in Dota 2 patch 7.41f (8 heroes), with the full change list and my take on each one.
All 16 item and 1 neutral item changes in Dota 2 patch 7.41f, with a short take on each.
Dota 2 patch 7.41f has no map changes, so here is what the patch does to the game as a whole.
My Mailgun login stopped working right after I moved my blog to Ghost 6, and Ghost 6 needs email to let staff log in. Here is how I set up Amazon SES with Terraform, added the DNS records at GoDaddy and pointed Ghost at the SES SMTP endpoint.
Regular Kite orders have no one-cancels-other, so a stop and a target placed together can leave you in a fresh position the other way. Here is the small Python watcher I run to cancel or shrink the surviving leg.
Ghost has to be upgraded to the latest minor of each major before the next one. Here is the script I used to step a Ghost 4 database through ghost:4, ghost:5 and ghost:6 containers, and the "Ghost booted" trap that made me run it twice.
I tried to turn llama3.2:1b into a pre-trade rule checker with an Ollama Modelfile. It passed 2 of 6 test cases, invented a margin check and said 174 is under 45. Here is the setup, the eval script and what I use instead.
This blog ran on a hand-built 2020 server with Ghost-CLI, Nginx, acme.sh and MySQL 5.7. Here is how I moved it to Docker Compose with Caddy, Ghost 6 and MySQL 8.4, checked the data and cut over by moving the Elastic IP.
My old Ghost server had Nginx, three acme.sh certificates and a root cron job. The new one has a Caddyfile of about ten lines that gets the certificates, renews them and redirects www and blog to the apex. Here is the file and how I checked it.
Our Flutter app kept the login token in SharedPreferences, wrote it to the device logs and allowed Android backups. None of it was obvious until a security review. Here is what we changed, with the code.
Before paying for a pentest, you can find most of the obvious problems in your AWS account yourself with read-only CLI calls. Here is the checklist I run, what each check looks for and how to keep it safe for production.
govulncheck only reports vulnerabilities your code can actually reach, which makes the output short enough to act on. Here is how I run it, why I scan the built binary and how a fixed vulnerability came back because of the Go version in go.mod.